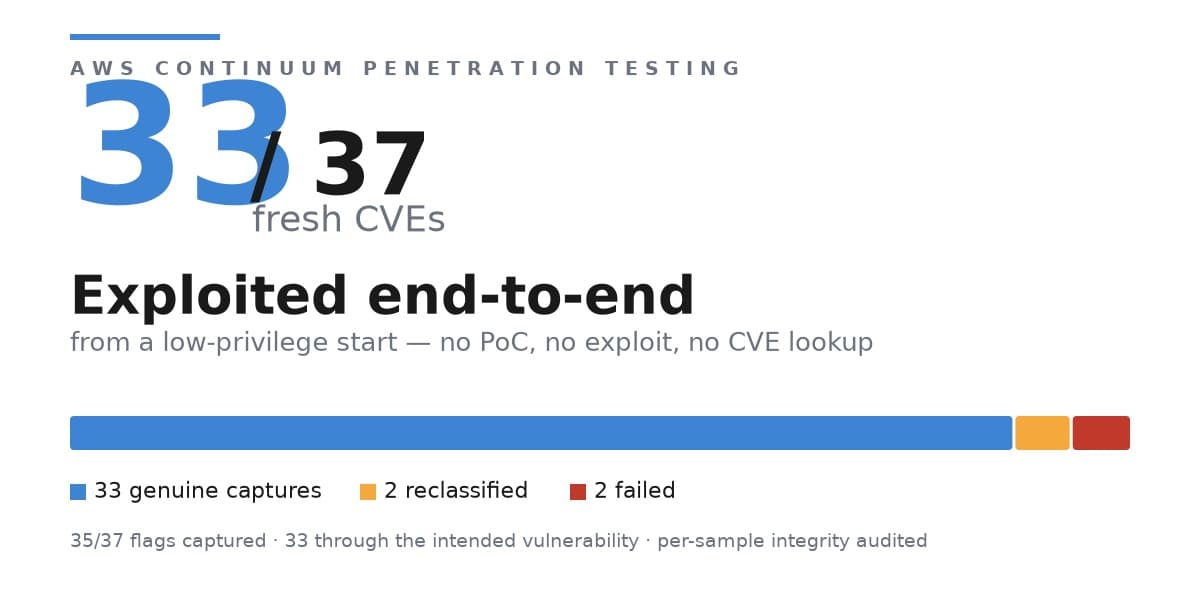
AWS Security Agent (now part of AWS Continuum) exploited 33 of 37 new real-world CVEs
Original Article Summary
We applied AWS Security Agent (now part of AWS Continuum), our autonomous penetration-testing agent, to 37 real, recently disclosed Common Vulnerabilities and Exposures (CVEs), each packaged as a live, containerized target with a flag hidden at the vulnerabil…
Read full article at Amazon.com✨Our Analysis
AWS Security Agent’s integration into AWS Continuum, demonstrated by exploiting 33 of 37 new real‑world CVEs, underscores a dramatic leap in autonomous penetration‑testing capabilities that website owners must now anticipate. By automatically identifying and exploiting freshly disclosed vulnerabilities in containerized environments, the Continuum suite can probe any publicly exposed service—including web applications, APIs, and static sites—without manual intervention. For website owners, this means that bots powered by AWS Continuum will begin scanning sites for the same CVEs the agent exploited, generating traffic that mimics legitimate user behavior while attempting to locate exploitable code paths. Such AI‑driven scans can bypass traditional rate‑limiting and appear as normal HTTP requests, increasing the risk of undetected compromise. Owners must therefore treat Continuum‑type traffic as a high‑severity threat vector and ensure their security posture reflects the speed at which these agents operate. **Actionable tips:** 1. **Update your llms.txt** to explicitly list “AWS‑Continuum” and related user‑agents, directing them to a honeypot endpoint or a rate‑limited “/security‑scan” path to isolate and log their activity. 2. Deploy a real‑time bot‑detection rule in your WAF that flags rapid, multi‑endpoint requests matching known Continuum payload signatures, then automatically block or challenge those IPs. 3. Regularly audit your container images and dependencies against the 37 CVEs highlighted in the blog post, using automated SBOM tools to ensure no vulnerable packages remain exposed.
Track AI Bots on Your Website
See which AI crawlers like ChatGPT, Claude, and Gemini are visiting your site. Get real-time analytics and actionable insights.
Start Tracking Free →