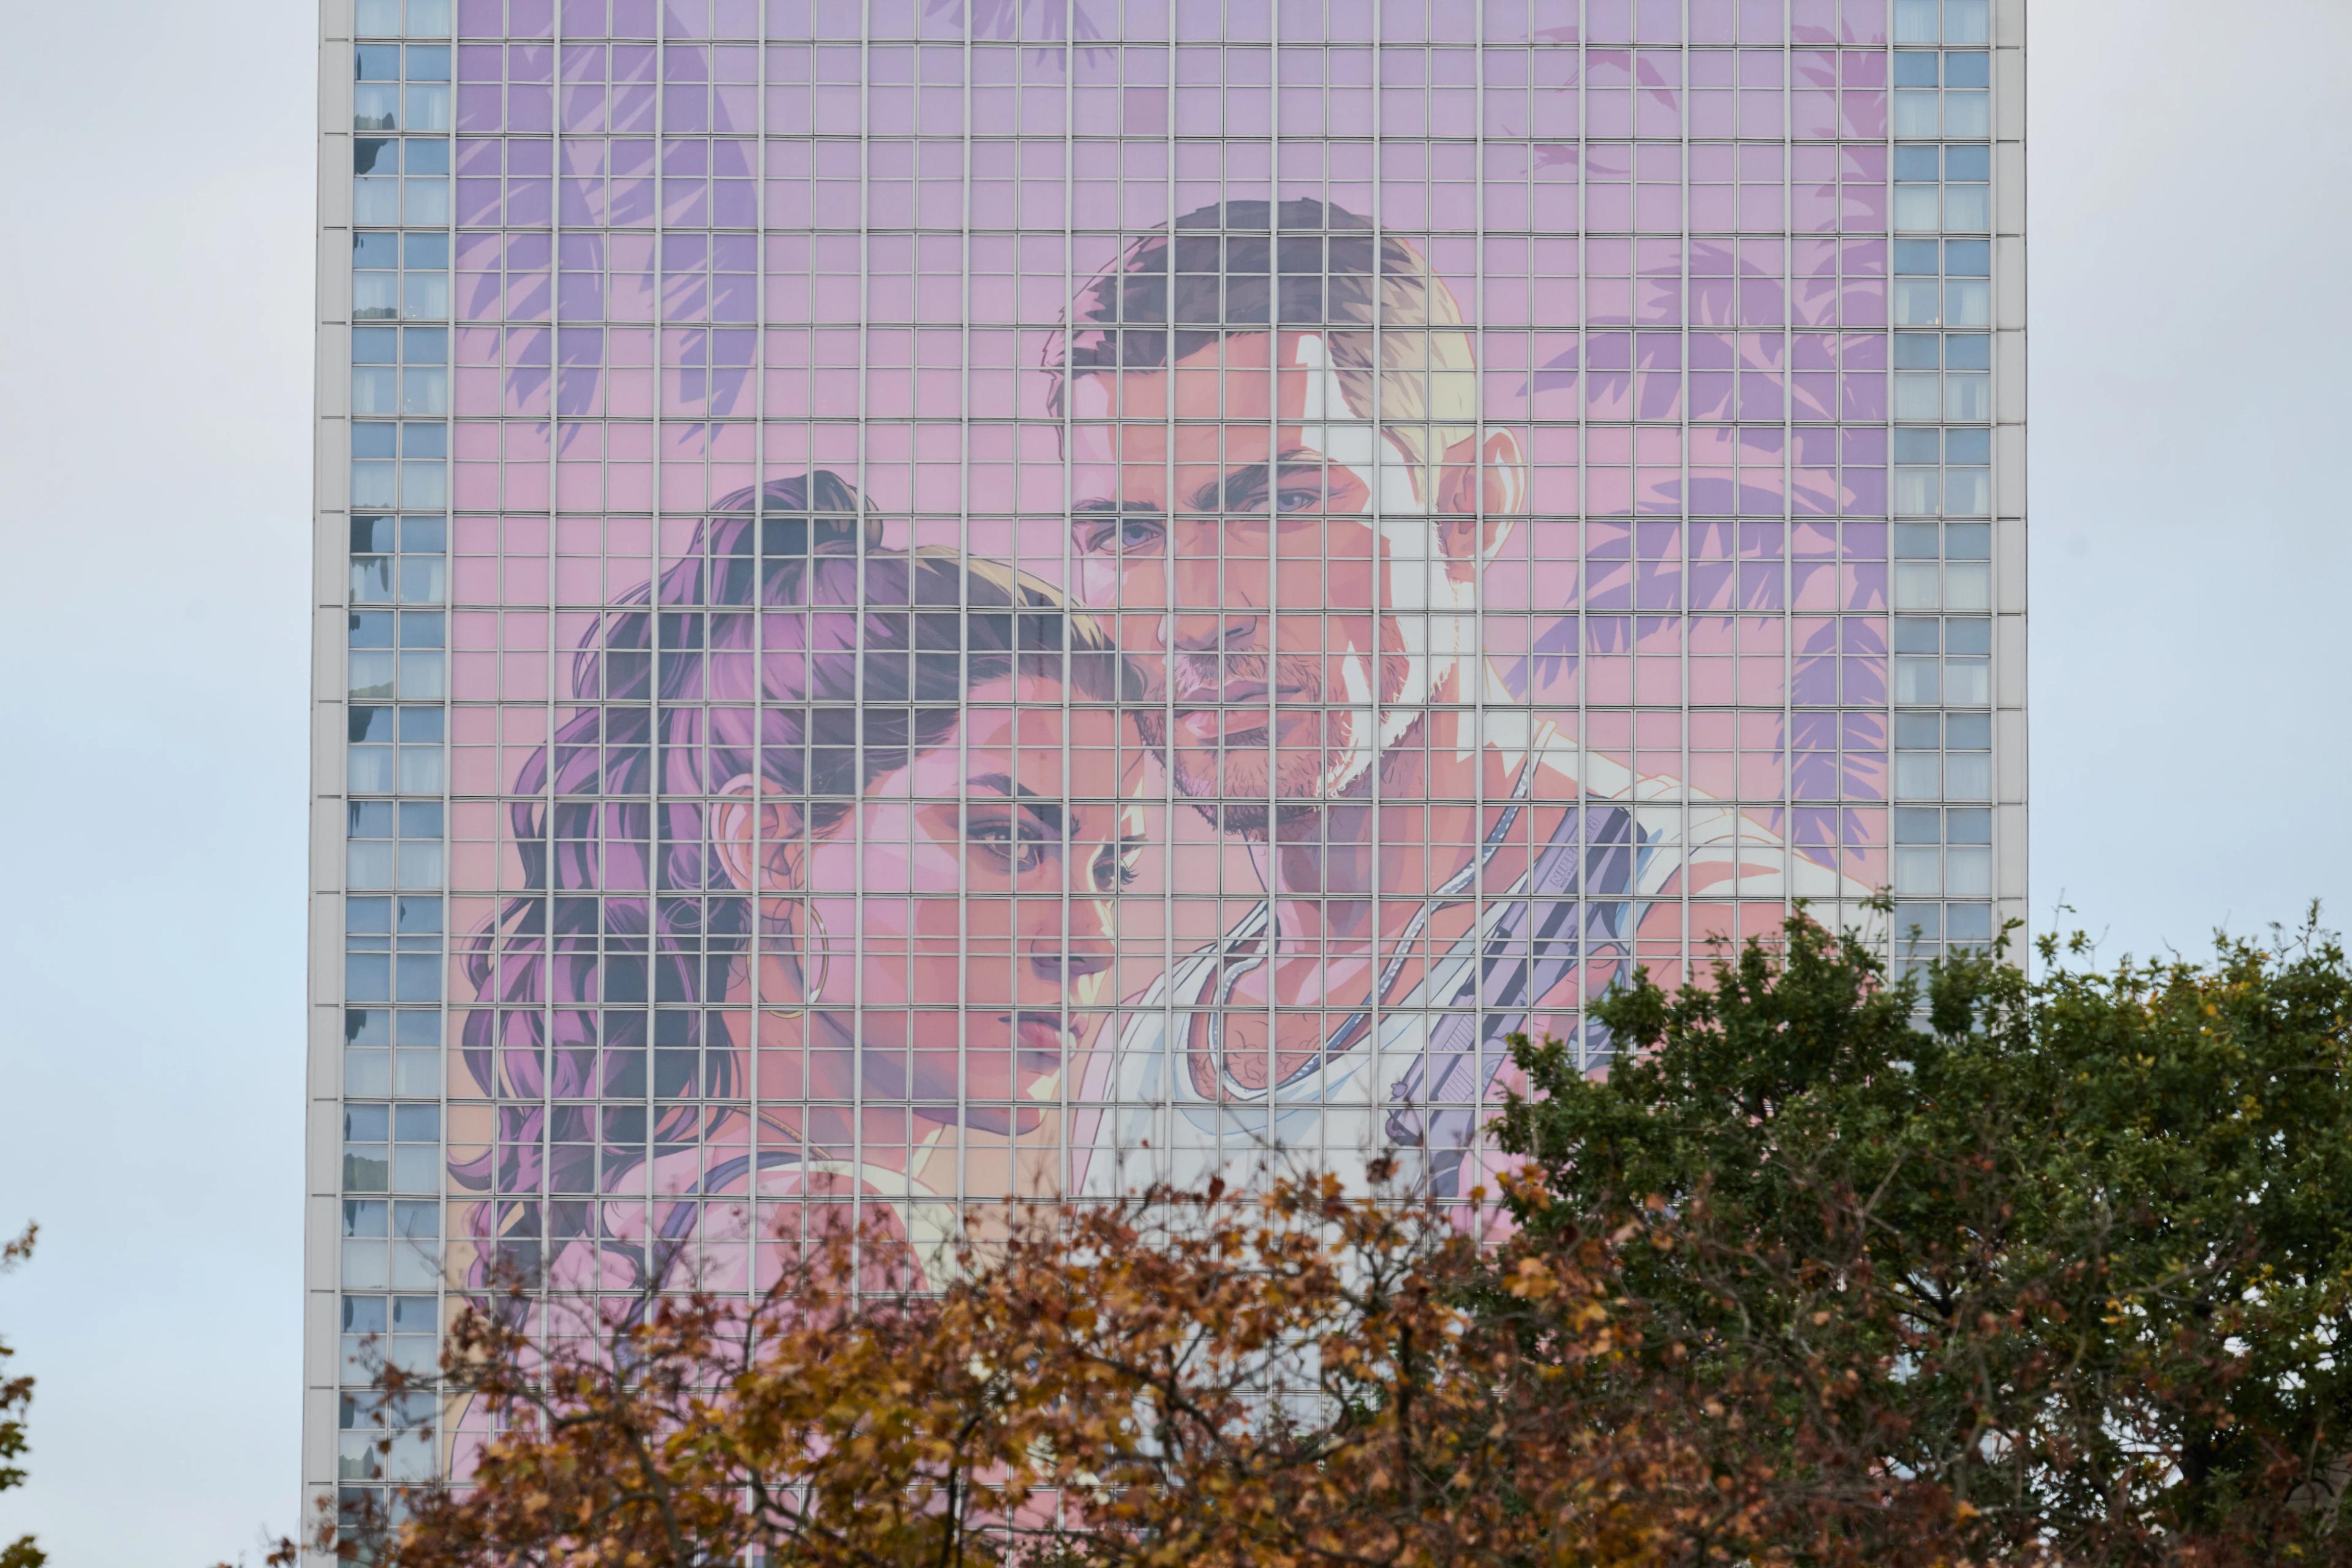
Grand Theft Auto made crime a game. AI is doing the same for hacking
✨Our Analysis
Artex's report that AI‑driven hacking tools now operate on three‑hour cycles, mirroring the “three‑hour clock” mechanic from Grand Theft Auto, highlights a new tempo in automated cyber‑attacks. For website owners this means that AI bots can launch coordinated intrusion attempts, credential stuffing, and content scraping in short, predictable bursts, overwhelming traditional rate‑limiting defenses. The rapid, recurring windows increase the likelihood of successful exploitation before security teams can react, especially on sites that expose APIs or login endpoints without robust bot detection. **Actionable tips:** 1. **Update your llms.txt** to explicitly disallow AI‑generated traffic from known hacking frameworks (e.g., add `User‑Agent: ArtexAI‑Bot` → `Disallow: /`), ensuring compliant bots are blocked at the crawl level. 2. **Implement time‑based throttling** that detects and caps requests during three‑hour intervals, automatically tightening limits when traffic spikes align with the identified attack windows. 3. **Deploy real‑time bot fingerprinting** that flags AI‑generated signatures (such as uniform request headers or rapid session creation) and routes them to a sandbox for deeper analysis, reducing exposure to automated hacking cycles.
Track AI Bots on Your Website
See which AI crawlers like ChatGPT, Claude, and Gemini are visiting your site. Get real-time analytics and actionable insights.
Start Tracking Free →