Trojanized Claude Code Extension Plants an SSH Backdoor
Original Article Summary
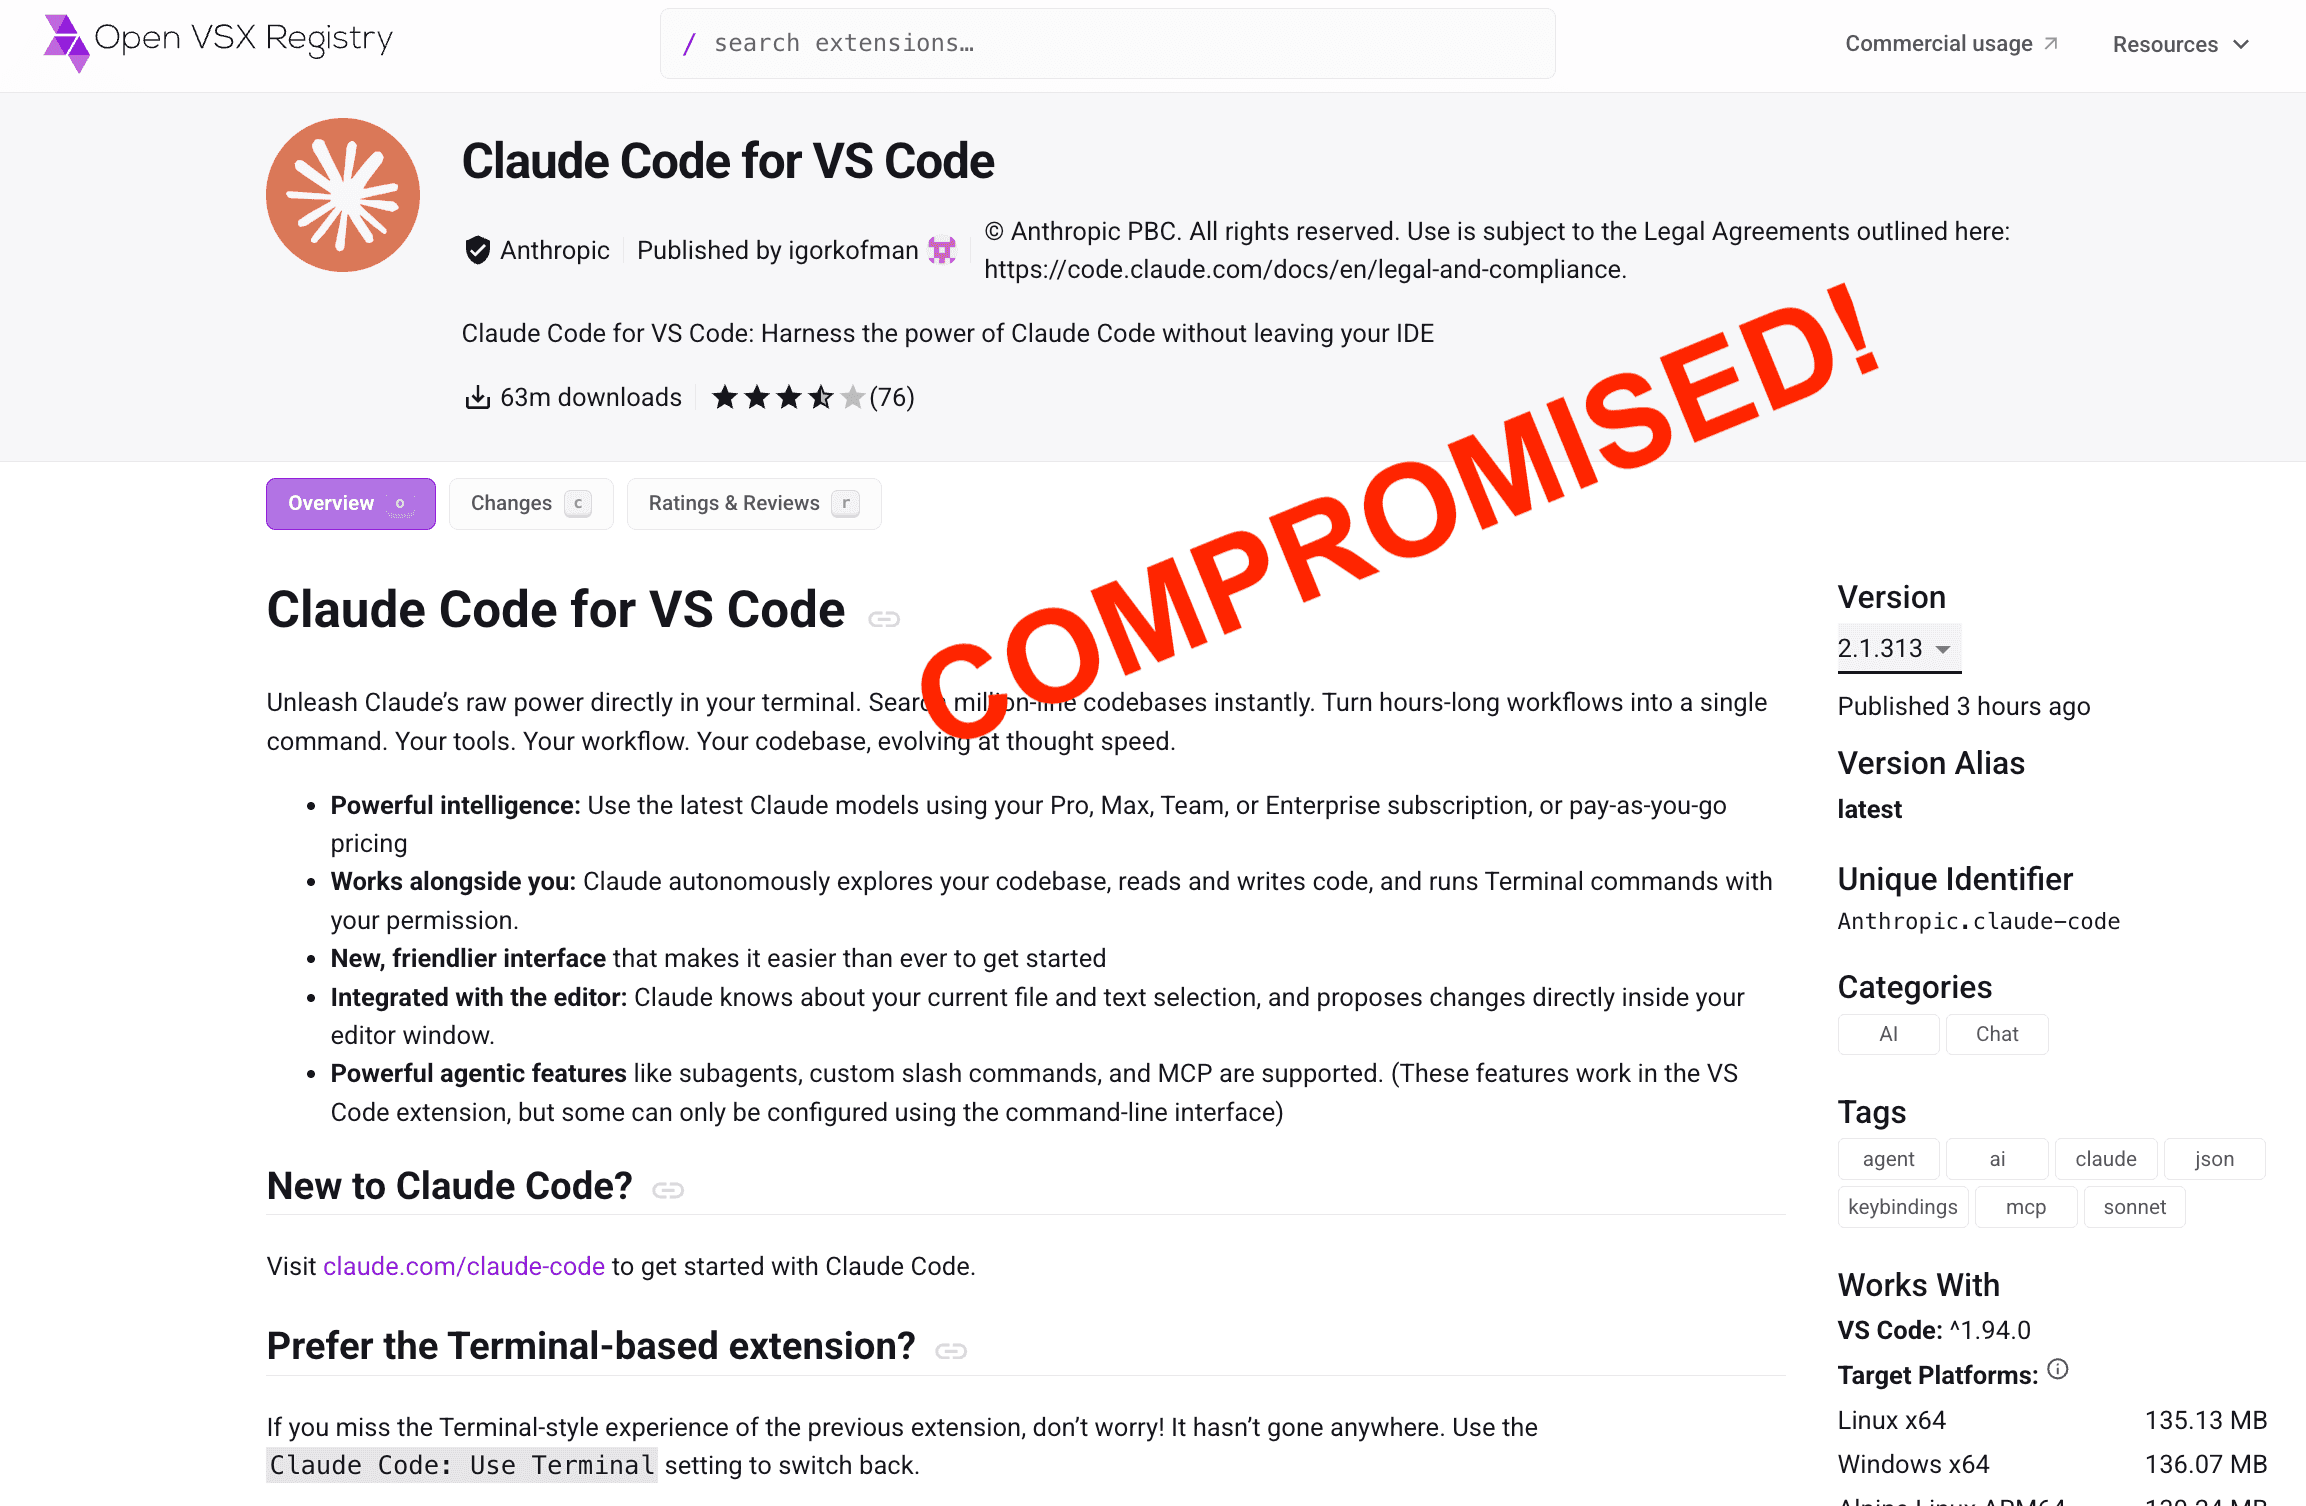
v 2.1.313 contains a loader that runs ahead of the real extension code adds an attacker key, opens a reverse tunnel, and sets persistence By c0a15726-c5b1-4b0d-85e6-fe15553df9e2 · 2026-10-30T09:42:00.000Z The official Claude Code VSCode extension was compromi…
Read full article at Opensourcemalware.com✨Our Analysis
Claude's official Code VSCode extension 2.1.313 was found to contain a hidden loader that injects an attacker‑controlled SSH key, opens a reverse tunnel, and establishes persistence on developers’ machines, effectively turning the IDE into a Trojanized backdoor. For website owners, this breach signals a new attack surface: compromised developer environments can be leveraged to exfiltrate site credentials, inject malicious scripts, or automate credential stuffing against your APIs. If a developer uses the tainted Claude extension to edit site code, the backdoor can silently push malicious code into your repositories, leading to AI‑driven bots that scrape or deface pages without detection. Moreover, the reverse SSH tunnel can be used to bypass traditional firewall rules, allowing bots to appear as legitimate traffic from trusted IP ranges. **Actionable steps:** 1. **Audit and lock down VSCode extensions** – enforce a whitelist in your CI/CD pipeline and require SHA‑256 verification of extension packages before installation. 2. **Update your llms.txt** to explicitly deny any AI agents originating from compromised development IPs, adding entries such as `User-Agent: Claude-IDE/* Disallow: /`. 3. **Implement bot‑traffic monitoring** that flags unexpected SSH‑tunneled connections or sudden spikes from internal IP ranges, enabling rapid isolation of potentially compromised developer machines.
Related Topics
Track AI Bots on Your Website
See which AI crawlers like ChatGPT, Claude, and Gemini are visiting your site. Get real-time analytics and actionable insights.
Start Tracking Free →